From 40,000 Alerts to the Whole Attack Story: How SIEM+ Campaigns Connect Alerts, Cases and Attackers
SIEM+ 1.1.0 campaigns group related cases so SOC teams see the attack story—MITRE ATT&CK rules, AI proposes, analysts decide.
James YipWe are a technology consulting firm specializing in SIEM+, SEKHMET AIoT, MSP services, and custom digital solutions. Leveraging advanced AI, cloud-native analytics, Microsoft technologies, and leading industry partnerships, we safeguard environments and build modern, highly efficient workspaces.
Trusted across Asia — Hong Kong · Singapore · Taiwan · Japan
Empower your business with enterprise-grade IT management, proactive cybersecurity, and robust cloud solutions tailored to your needs.
Managed SIEM, mini-SOC operations, alert triage, and incident response powered by Agentic AI, Devo, and Microsoft Sentinel.
Dedicated support, Ask-The-Expert consulting, and BAU management with deep Azure and Microsoft 365 expertise.
Seamless, secure transition of workloads, email, and archives to Azure and Microsoft 365.
Bespoke software application design, database performance tuning, and optimization.
Explore our proprietary solutions and cutting-edge partner technologies designed to solve complex business challenges.

An advanced AIoT solution bridging physical assets and digital intelligence.
Learn more
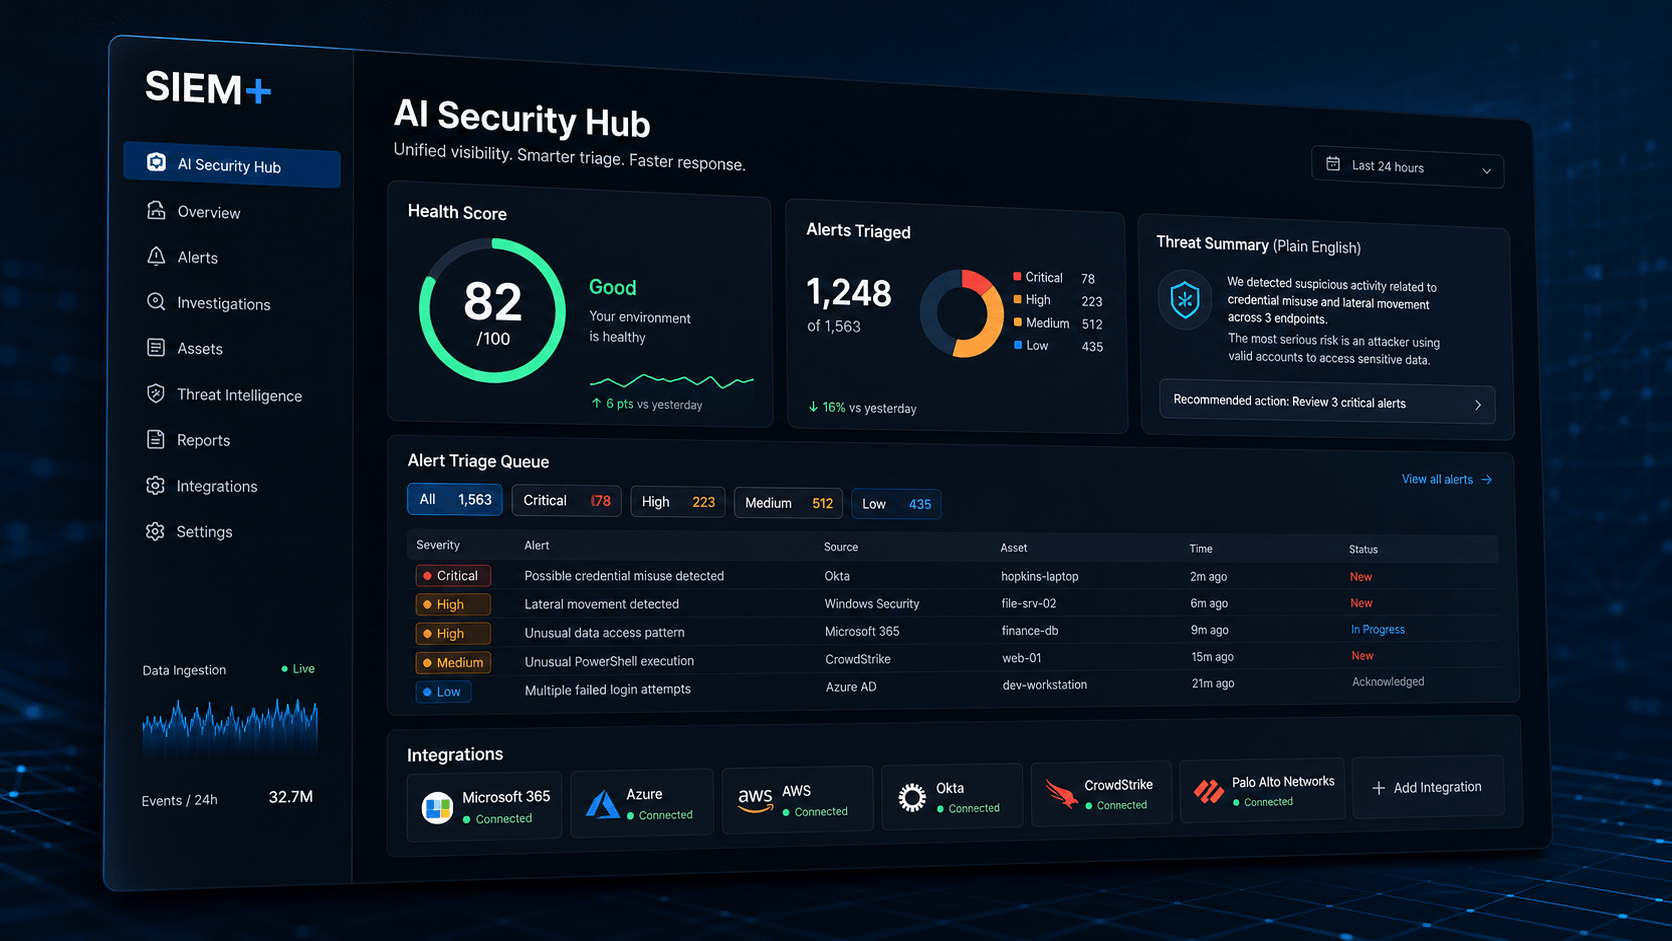
AI Security Hub for growing teams that overlays existing SIEM tools including Devo and Microsoft Sentinel, triages alerts, translates threats, scores posture, and guides remediation. Plans from $300/mo.
Learn more
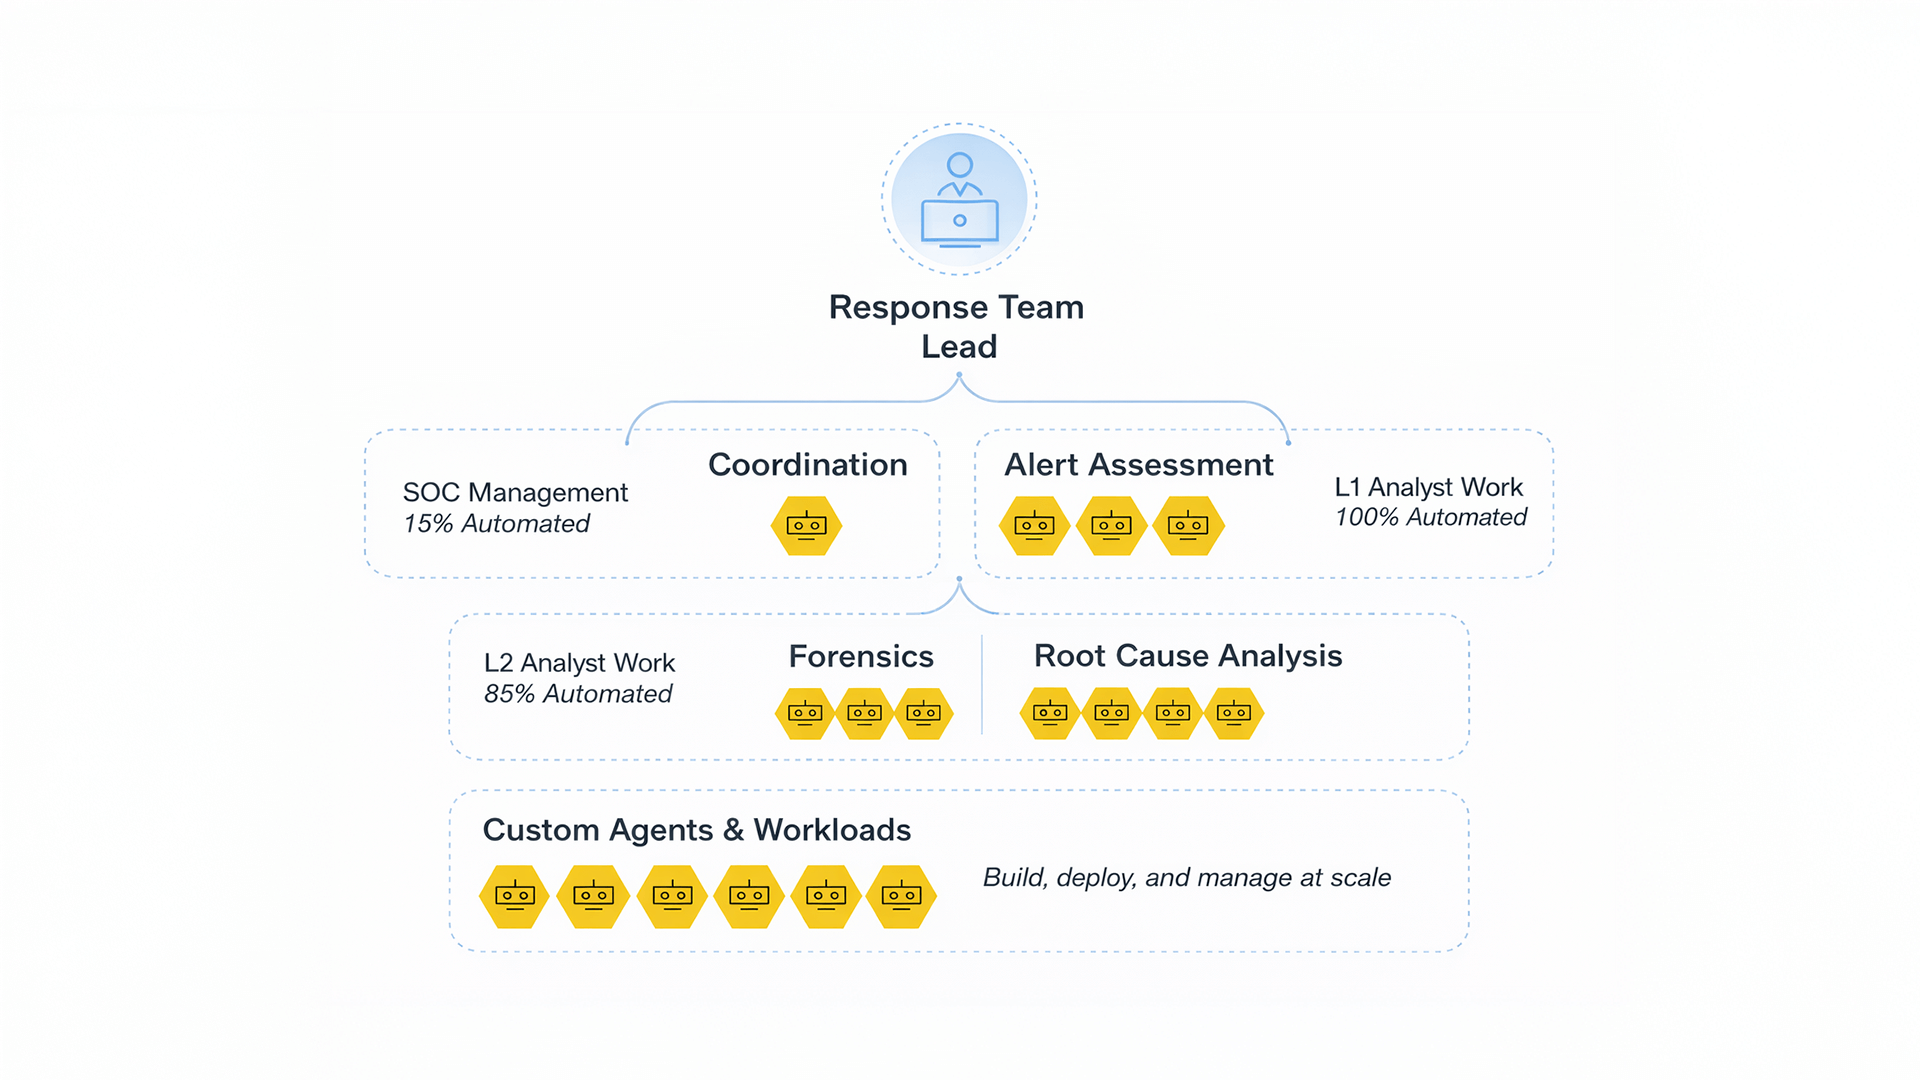
The world's first Agentic AI Log Intelligence Platform with a 48-hour deployment guarantee.
Learn more
Transformative intranet systems and centralized email signature management solutions.
Learn more
With a global footprint and a team of certified engineering experts, Eventus is dedicated to helping businesses grow. We combine strategic IT consulting, industry-leading security practices, and custom software engineering to deliver high-impact results.
Check out our latest blog posts on Eventus Blog for the latest news and updates.
SIEM+ 1.1.0 campaigns group related cases so SOC teams see the attack story—MITRE ATT&CK rules, AI proposes, analysts decide.
James YipMid-October 2026 Fortinet PSIRT advisories illustrate how vendor patch waves raise firewall and SIEM noise. An AI triage layer on your existing SIEM helps without rip-and-replace.
James YipEventus shares how Defender XDR and Microsoft Sentinel can help investigate phishing campaigns by scoping recipients, URL clicks, and post-click sign-ins, with practical SIEM+ triage.
James YipJapan's National Cybersecurity Office has confirmed multiple data thefts, including compromises through the supply chain, and asked executives to treat cybersecurity as a management issue. Five questions leadership should be able to answer this week, and how an AI triage layer on an existing SIEM helps with visibility and evidence.
James YipEventus is starting operations in Jakarta, Indonesia, opening a new chapter in connecting with businesses and partners in the region.
James YipA new Qiita article explains how Microsoft Sentinel user behavior analytics can use ASIM Authentication to avoid raw-table dependencies and handle diverse authentication sources.
James YipTalk to our team about technology consulting, SIEM+, SEKHMET, and Microsoft-centric IT services across Hong Kong, Singapore, Taiwan, and Japan.
Talk to an Expert